Skip to content
← All posts

#Windows 11

4 min read

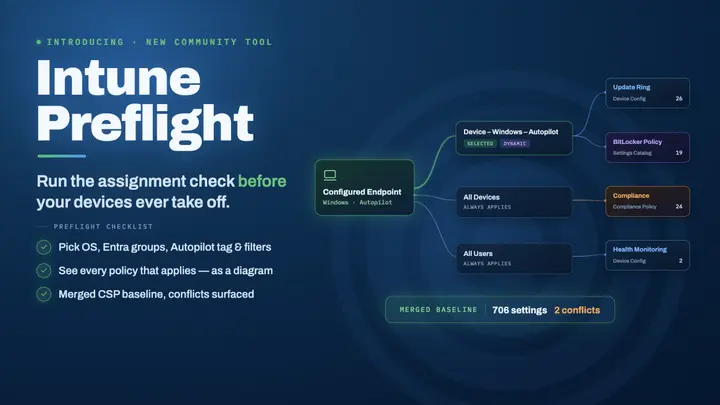
Introducing Intune Preflight: Simulate Your Endpoint’s Merged Baseline Before You Deploy

After roughly a year of writing deep-dive Intune content here on malinoski.me — posts on Assigned Access kiosks, Intune-based McAfee removal, policy conflicts, Autopatch deployments, and the eternal “why isn’t this device getting what I assigned?” question — I kept running into the same fundamental friction. Intune’s admin center is fantastic for creating policy, but…
8 min read

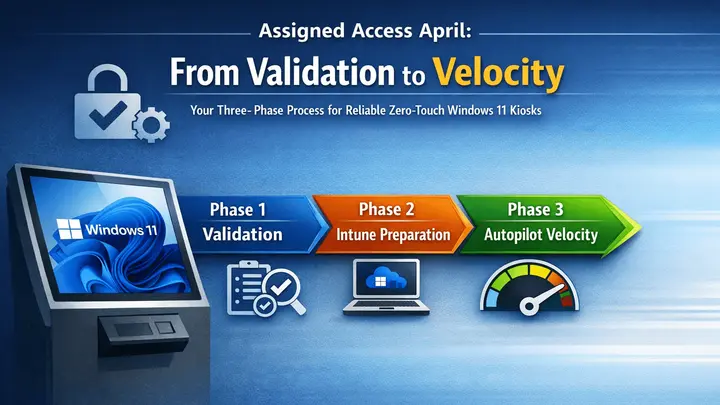
Assigned Access April: From Validation to Velocity – Your Three-Phase Process for Reliable Zero-Touch Windows 11 Kiosks

If you’ve been following along this month, you already know the story: we’ve spent the entire month of April diving deep into Assigned Access—the Windows 11 technology that powers reliable, locked-down kiosks for public-facing, frontline, and general-use devices. From the very first kickoff post (where we looked at why the old Intune Kiosk Templates don’t…

3 min read

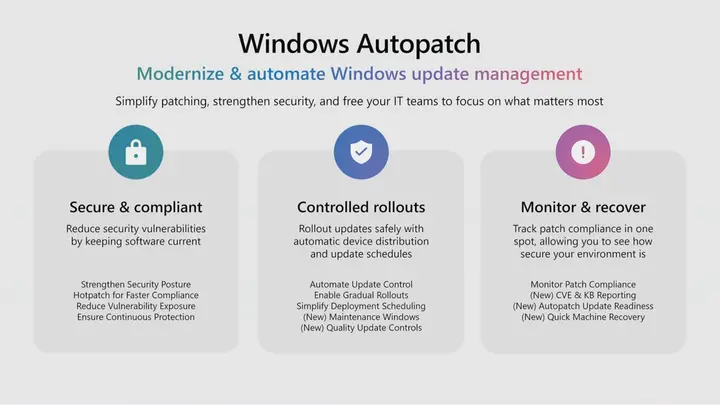
Windows Autopatch Reports Are Live – Time for Your Endpoints to Join the Journey

If you blinked (👀) this week, you might’ve missed it—perfect Read-Only Friday material. The new Windows Autopatch update readiness reports hit general availability, and honestly, these are the kind of insights Intune admins have been asking for forever. Cassidy Fein at Microsoft announced the welcome addition Intune on the Windows IT Pro Blog—definitely worth a…

5 min read

Mastering Windows Feature Updates – A Health Check for Your Intune Policies

As Microsoft shifts us toward cloud-managed endpoints via Intune, questions about fine-tuning these policies keep popping up – specifically regarding feature updates; uncontrolled feature updates can cause unsanctioned releases, leading to instability and poor user experiences Hey everyone, it’s been a bit since my last post on leveraging Autopatch to smoothly transition from Windows 10…